Built‑In Magento Defense
Built‑In Magento Defense
Magento defense in depth — CIS-hardened OS, CrowdSec WAF, rate limiting, bot challenges. Production defaults that are audit-ready, not an upgrade tier.

Edge Defense
Edge Defense
Three independent layers in front of your application — a network firewall, an application firewall, and IP-level threat intelligence. Different jobs, different traffic, all on by default. Read the CrowdSec docs.
Network Firewall
UFW blocks everything except the ports your store actually serves on, default-deny by default. No public SSH port, no exposed admin panels. Attackers do not get to start the conversation on closed ports.
Application Firewall (WAF)
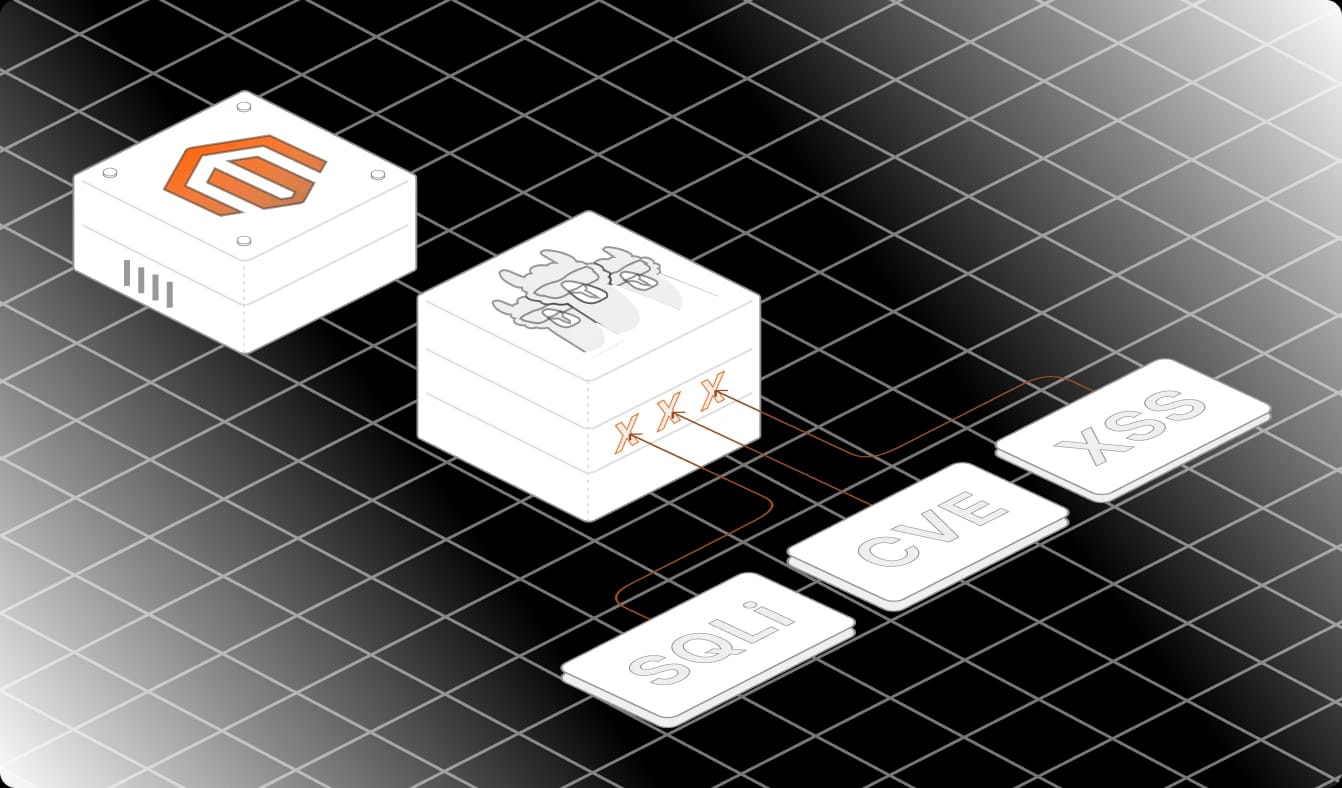
CrowdSec AppSec runs the OWASP Core Rule Set inline, plus virtual-patch rules that block known CVEs the moment they are published. SQLi, XSS, RCE, and path traversal are blocked at the edge before reaching Magento.
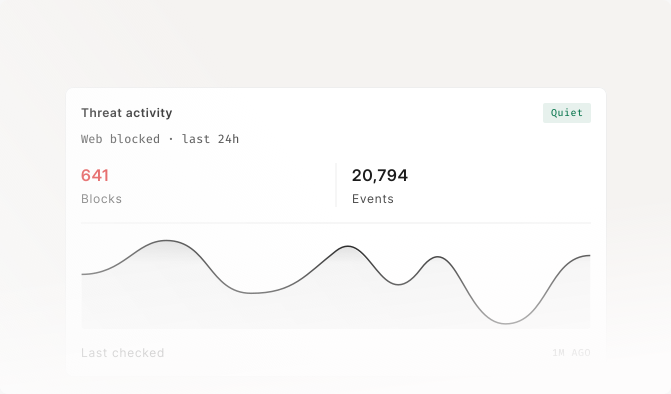
Community Threat Intelligence
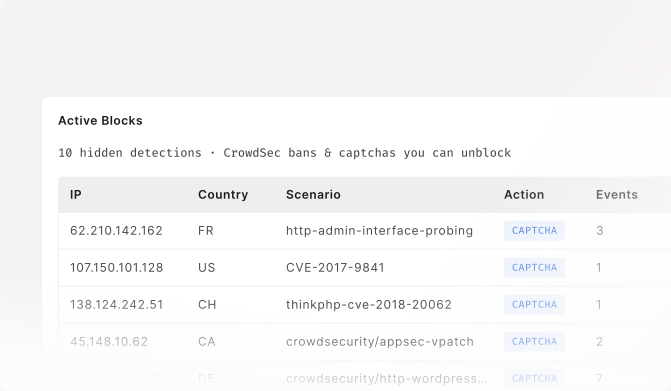
CrowdSec reads access logs for known attack patterns and blocks bad IPs before they reach your application. The threat feed is shared from thousands of installations — your environment benefits from attacks aimed at others.
Bot Mitigation and Hardening
Bot Mitigation and Hardening
What sits underneath the edge — bot challenges, explicit rate ceilings, hardened OS, isolated containers. Most automated traffic dies before reaching the application layer. See how OpenResty + Lua handle PoW and rate limiting, or read CIS hardening for what the Ubuntu baseline locks down by default.
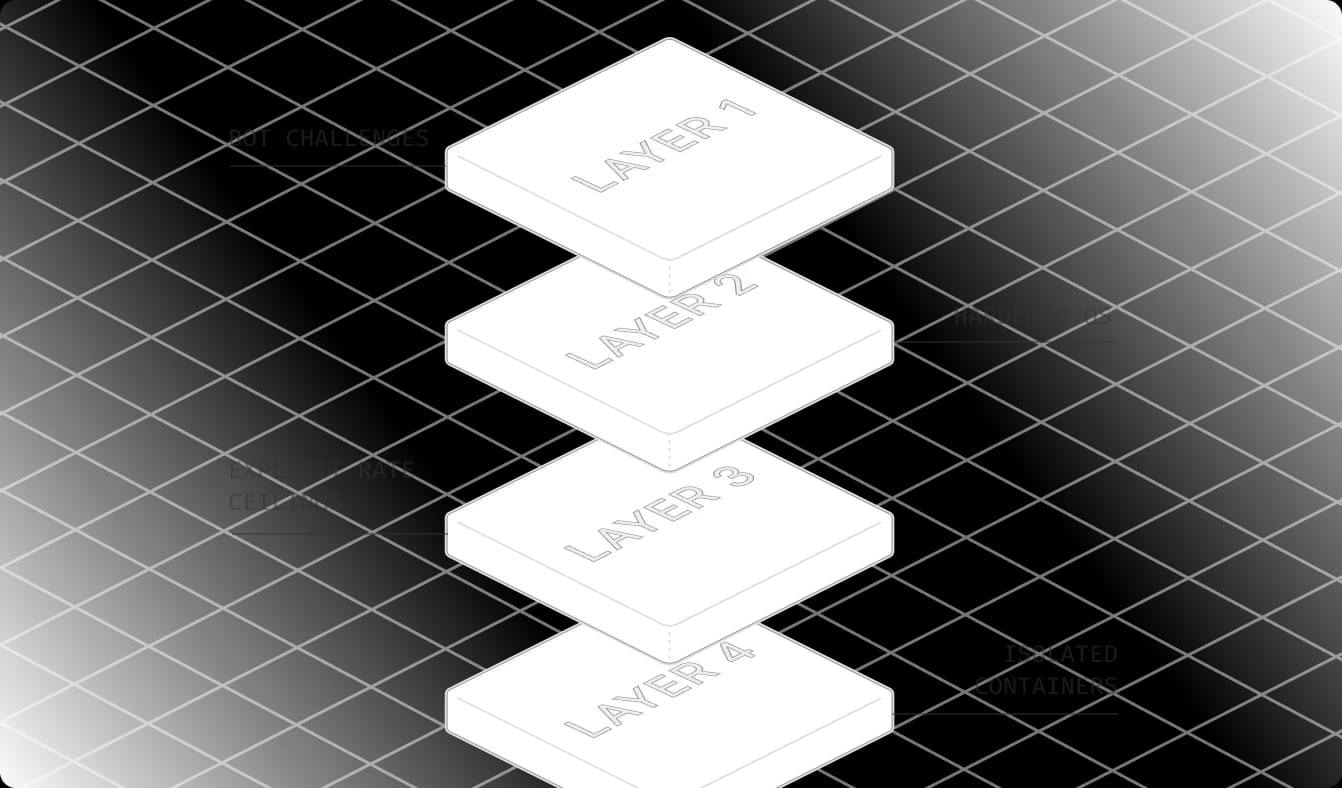
Bot Filtering
Suspected bots solve a SHA-256 Proof-of-Work challenge before reaching the application — real users never see it. FCrDNS verifies claimed bots (Googlebot, Bingbot) by reverse DNS. OpenResty rate-limits at 50 req/sec, 300 burst.
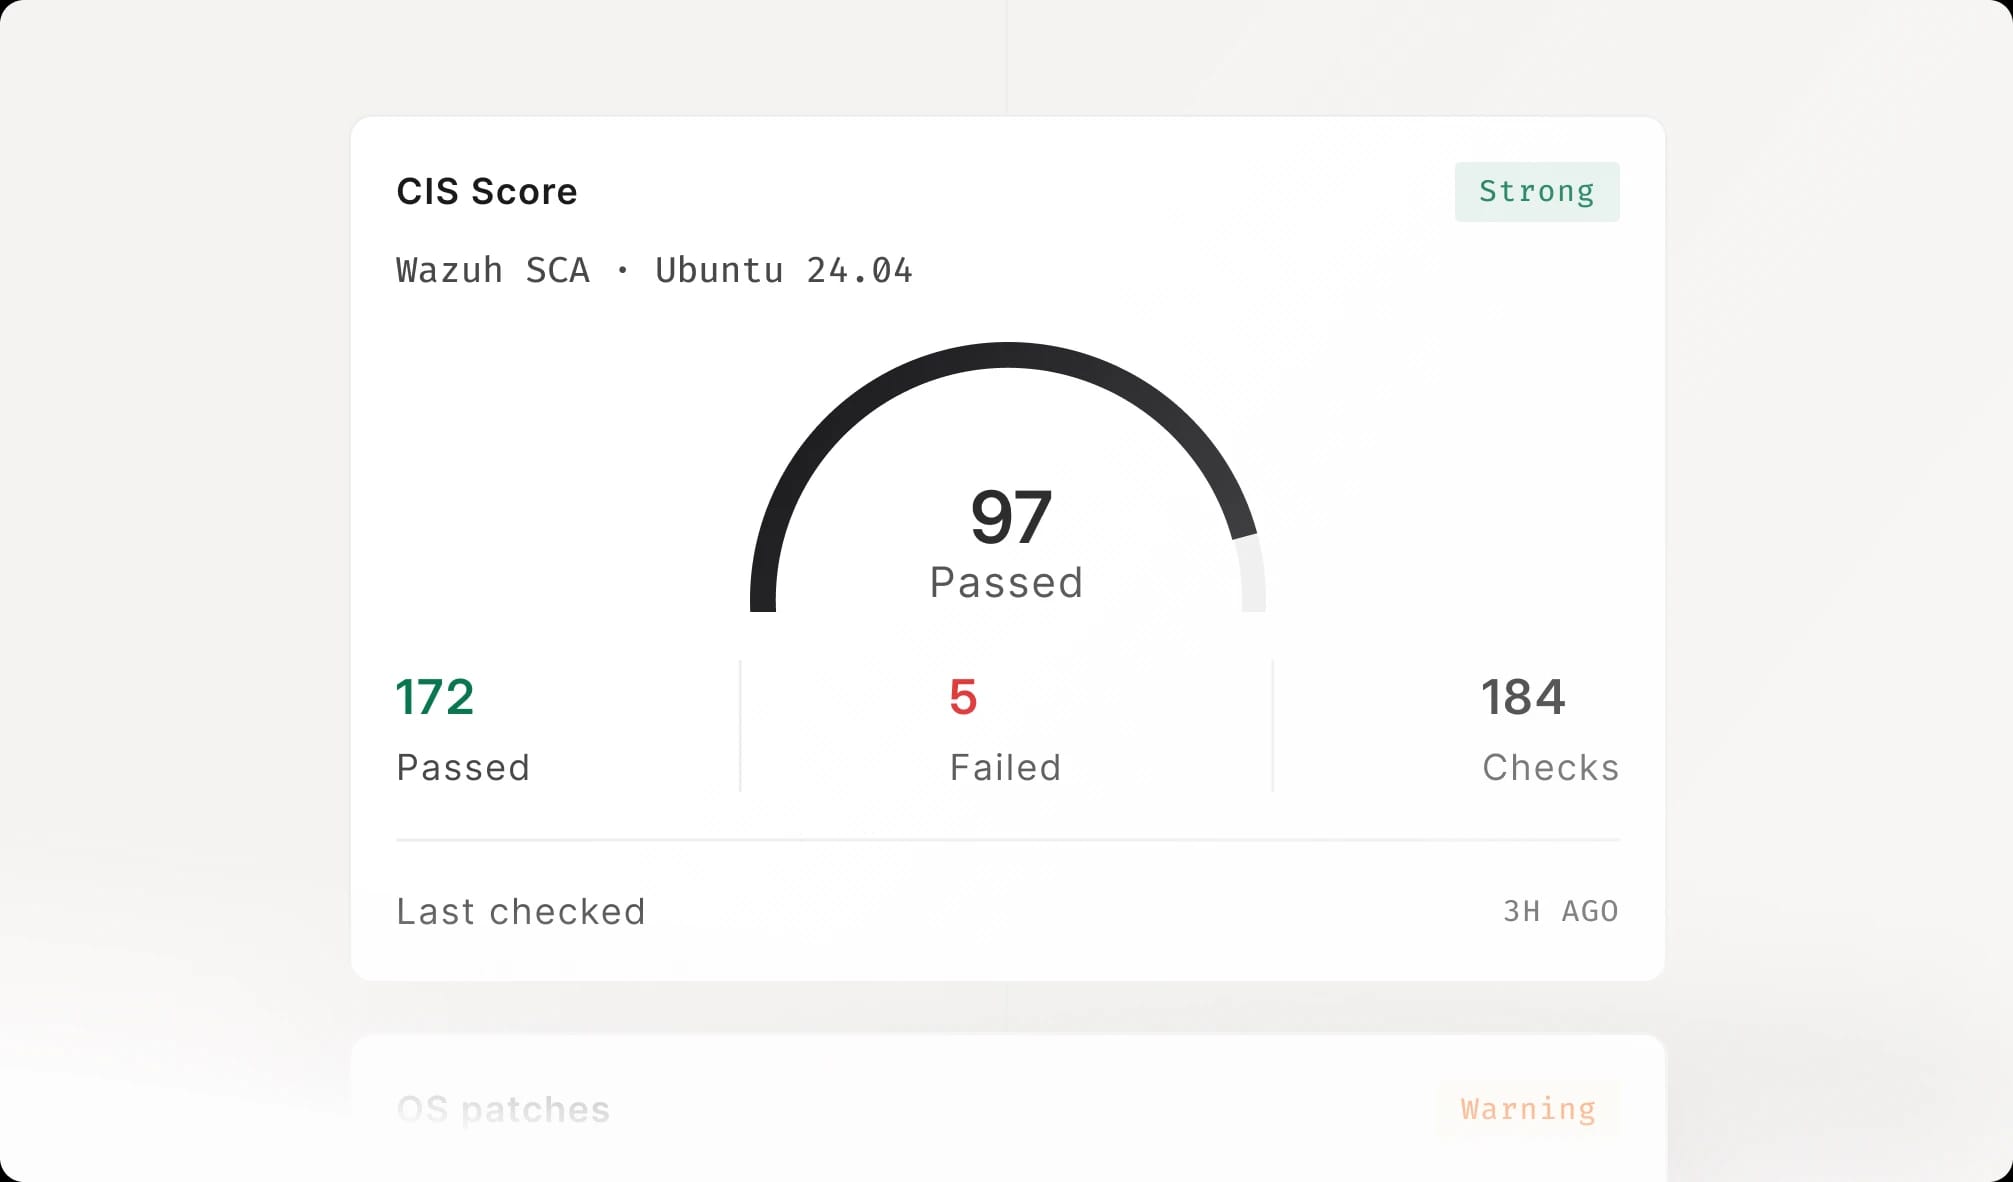
CIS-Hardened Ubuntu
Ubuntu hardened to the CIS Benchmark v2.0.0 standard — SSH key-only access, strict password policy, kernel modules locked at boot, and continuous file-integrity monitoring. Every server, by default.
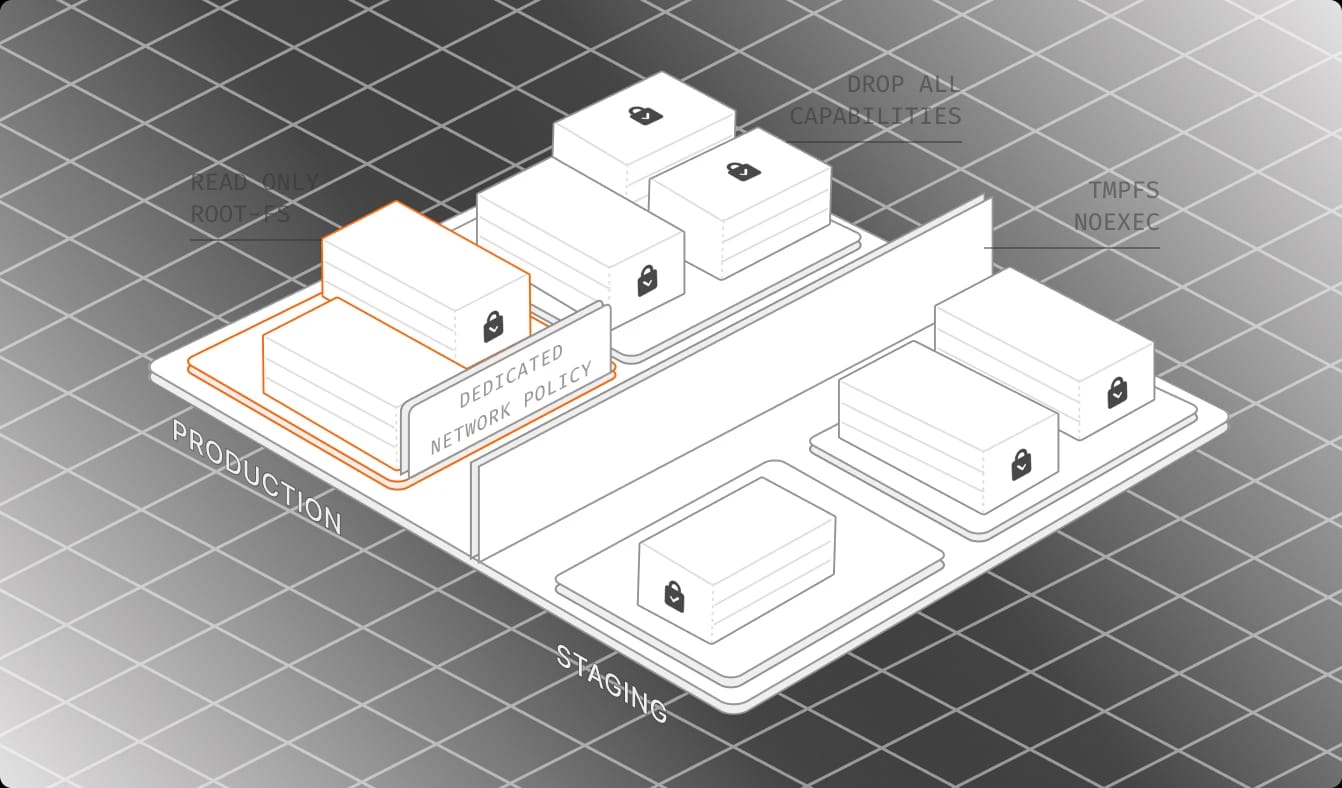
Container Security
Every container drops every Linux capability by default. Read-only root filesystems, tmpfs noexec/nosuid mounts, dedicated networks per environment. A breach in one container does not reach the others.
See Also
See Also
Different angles on the same environment — sibling infrastructure topics worth a look.
Magento Observability
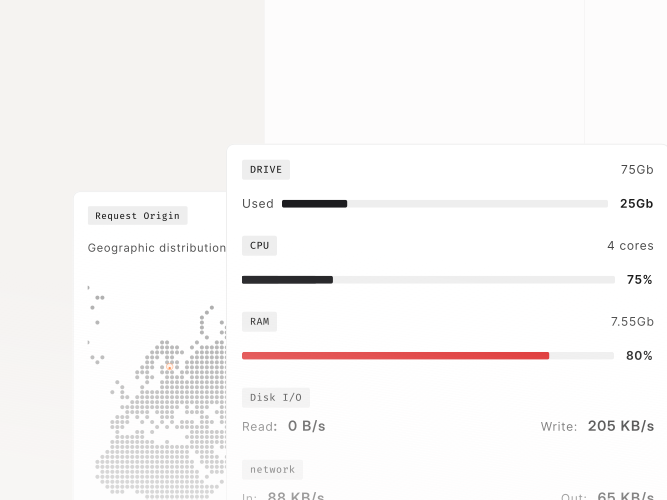
Real-time CPU, memory, container, and log streams from every environment.
Magento Operations Automation
Automatic SSL renewal, encrypted backups, 1-click provisioning, container updates.