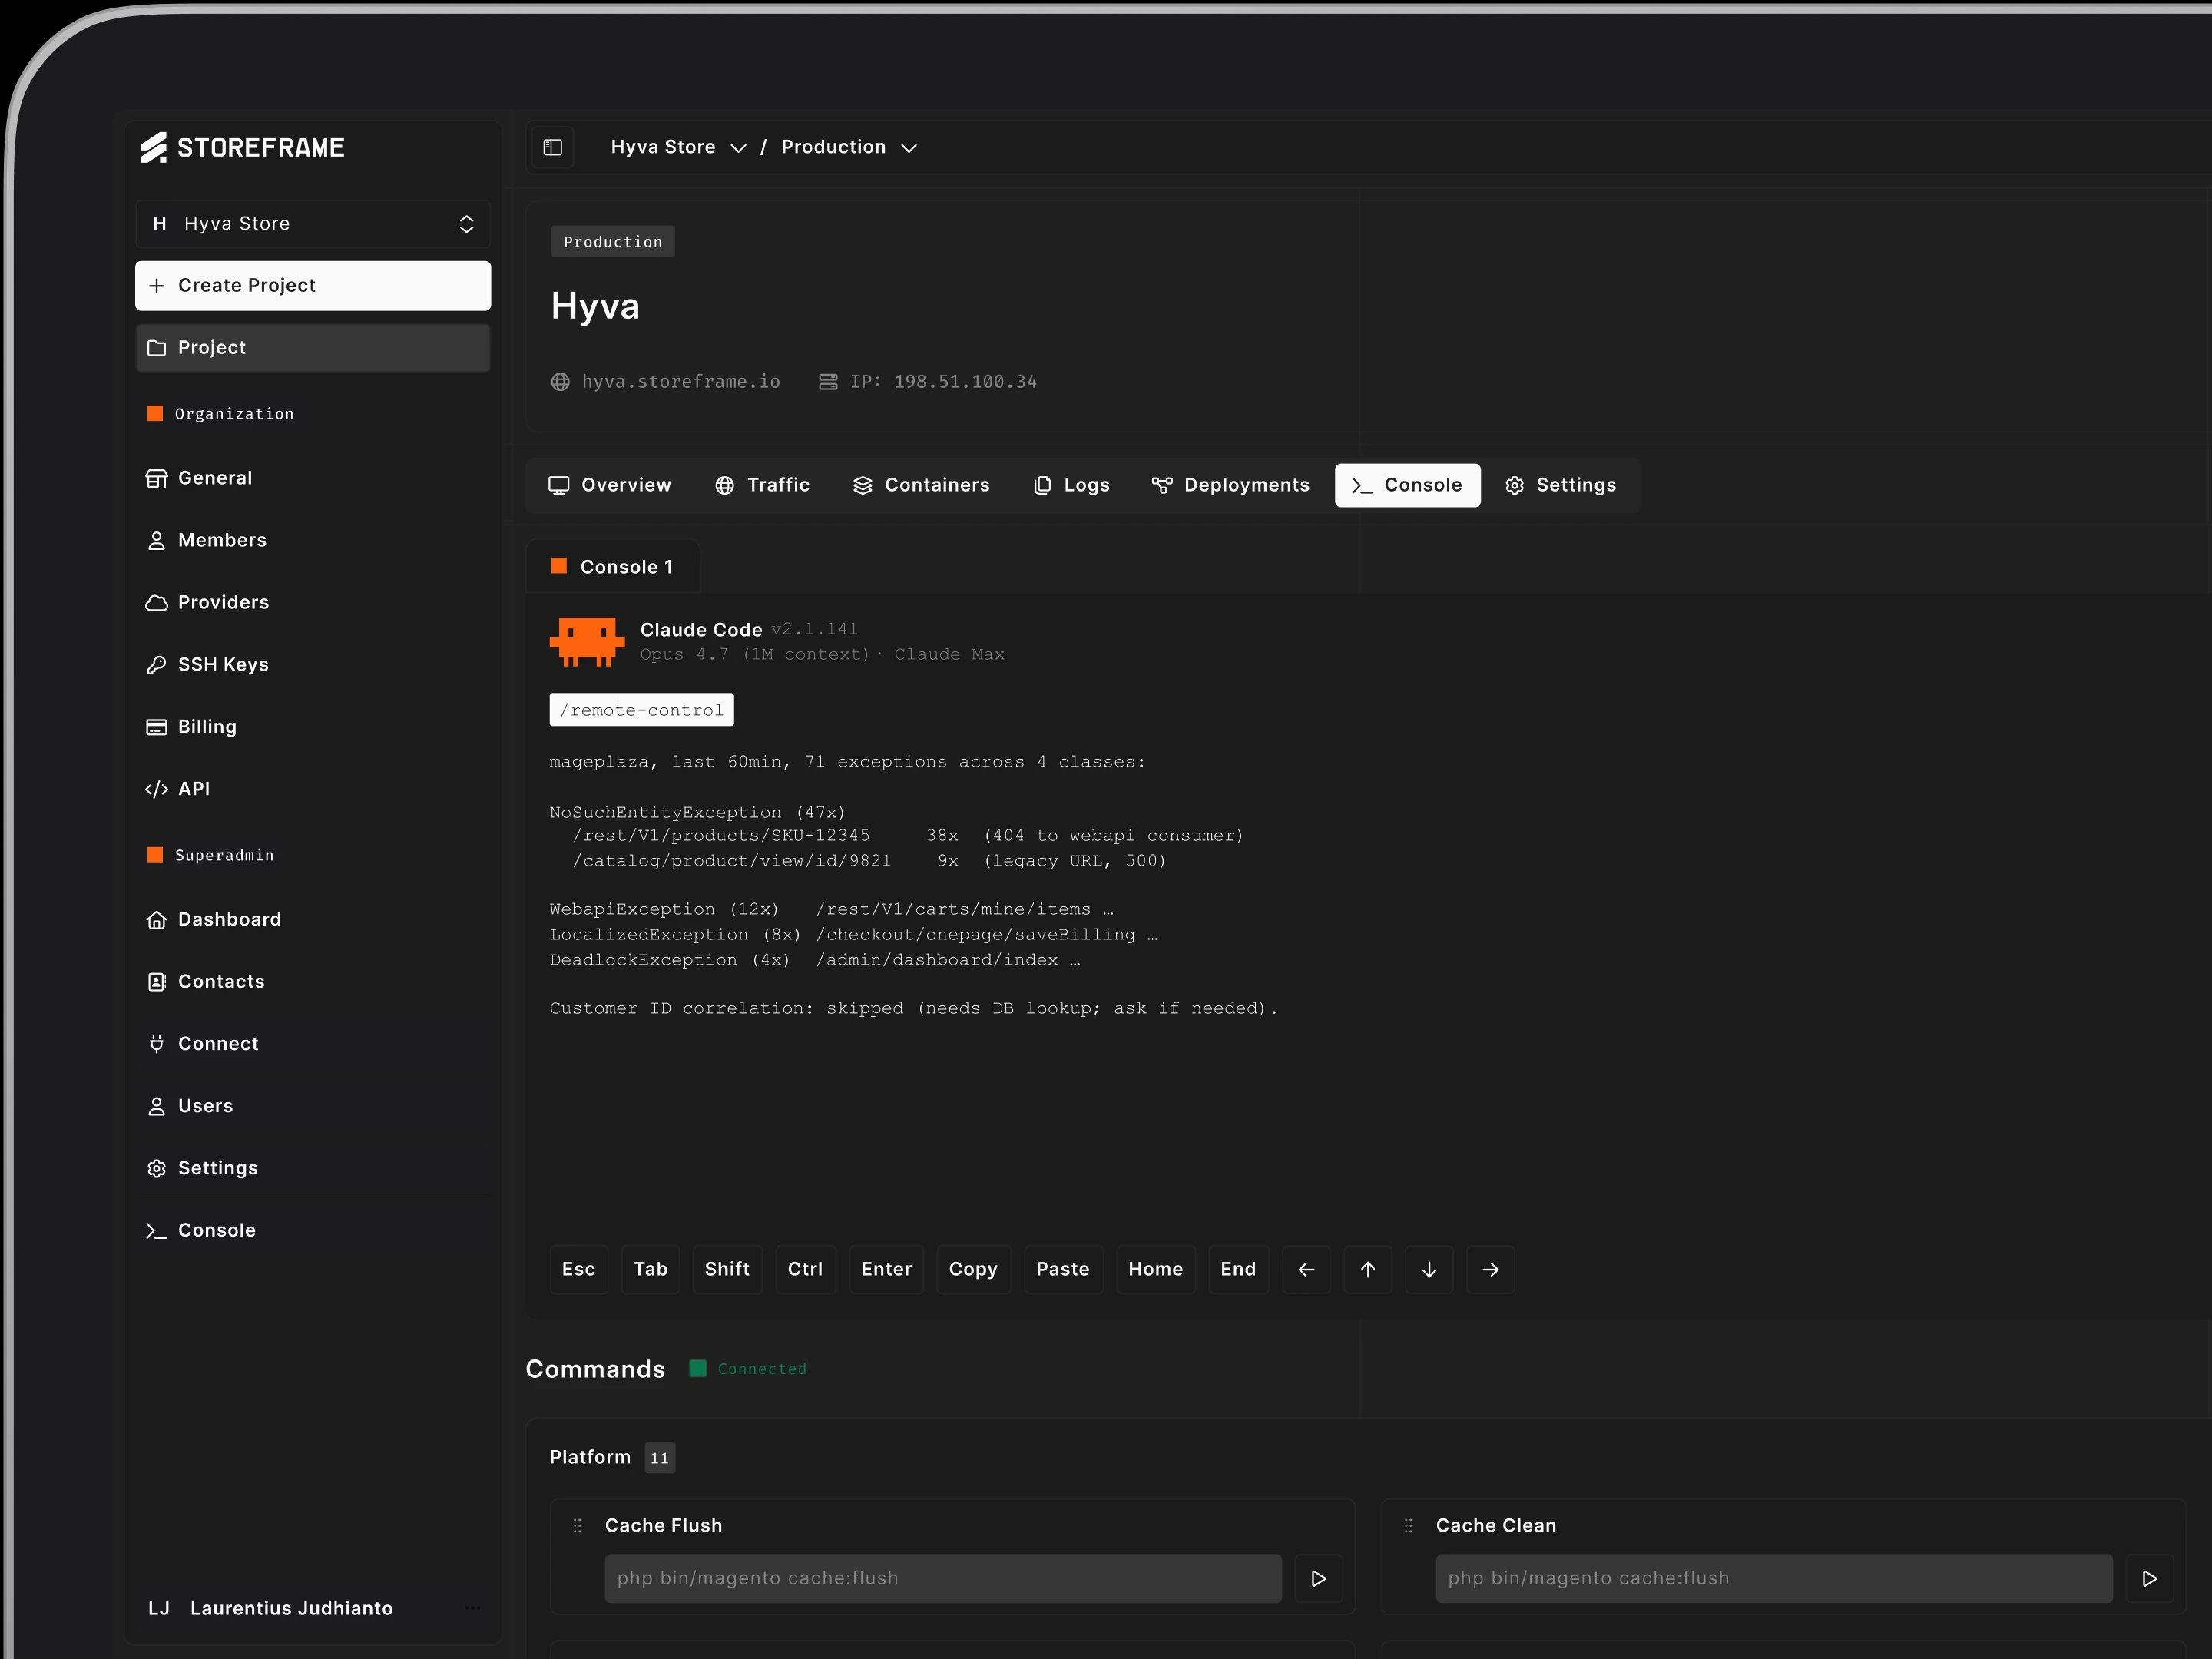
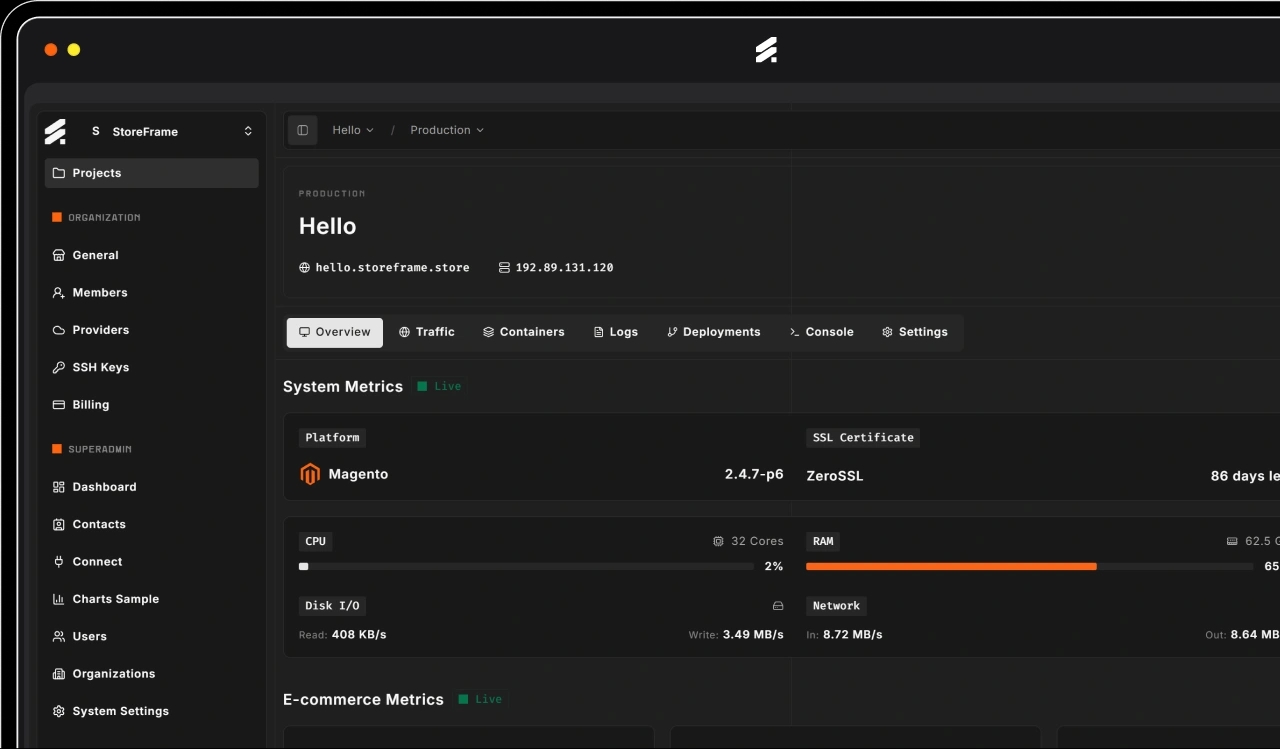
An AI-Native Containerized Stack, Auto Tune
An AI-Native Containerized Stack, Auto Tune
OpenResty, Varnish, FrankenPHP, MariaDB, OpenSearch, RabbitMQ, CrowdSec, Wazuh — wired together, auto-tuned at provision, re-tuned on resize. CIS-hardened, audit-ready, observable on a 3-second cadence. ARM and x86, full root.
Five Pillars of StoreFrame Infrastructure
Five Pillars of StoreFrame Infrastructure
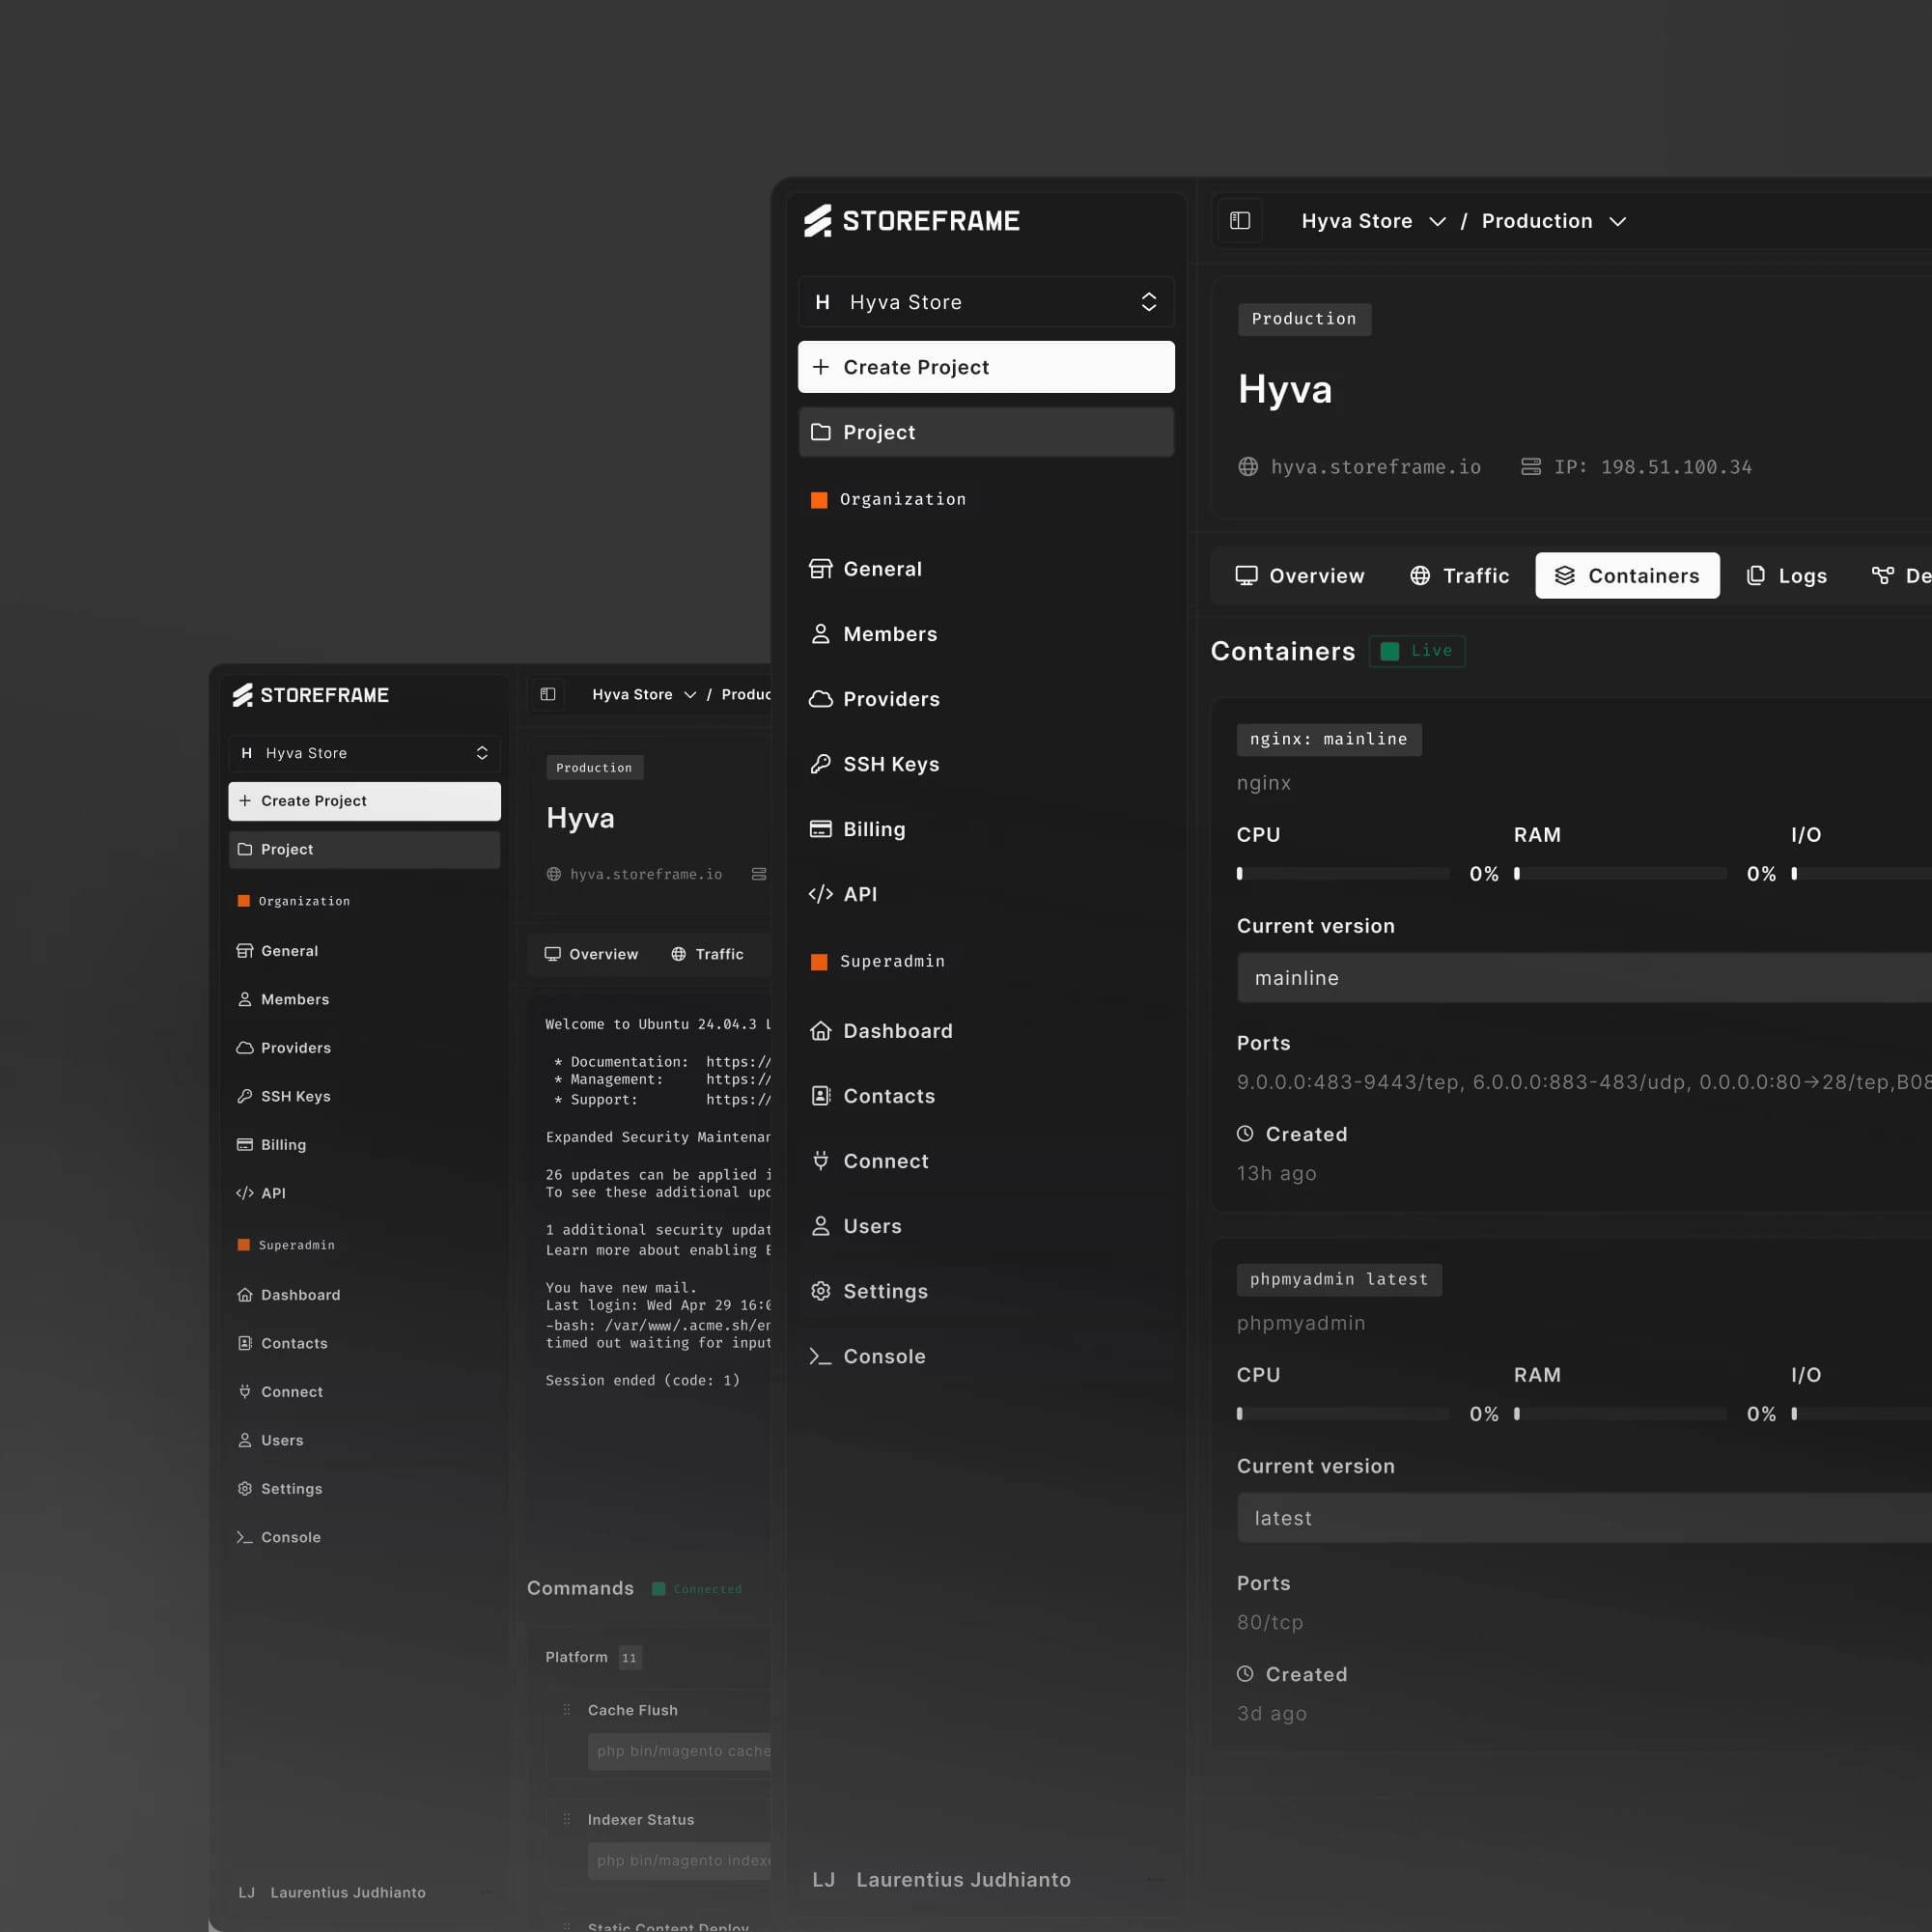
Built for AI, the containerized stack, real-time observability, layered security, and automation — five pillars on every environment, on by default. Read the full containerized stack docs or the provisioning lifecycle.
AI-Native Technology Stack
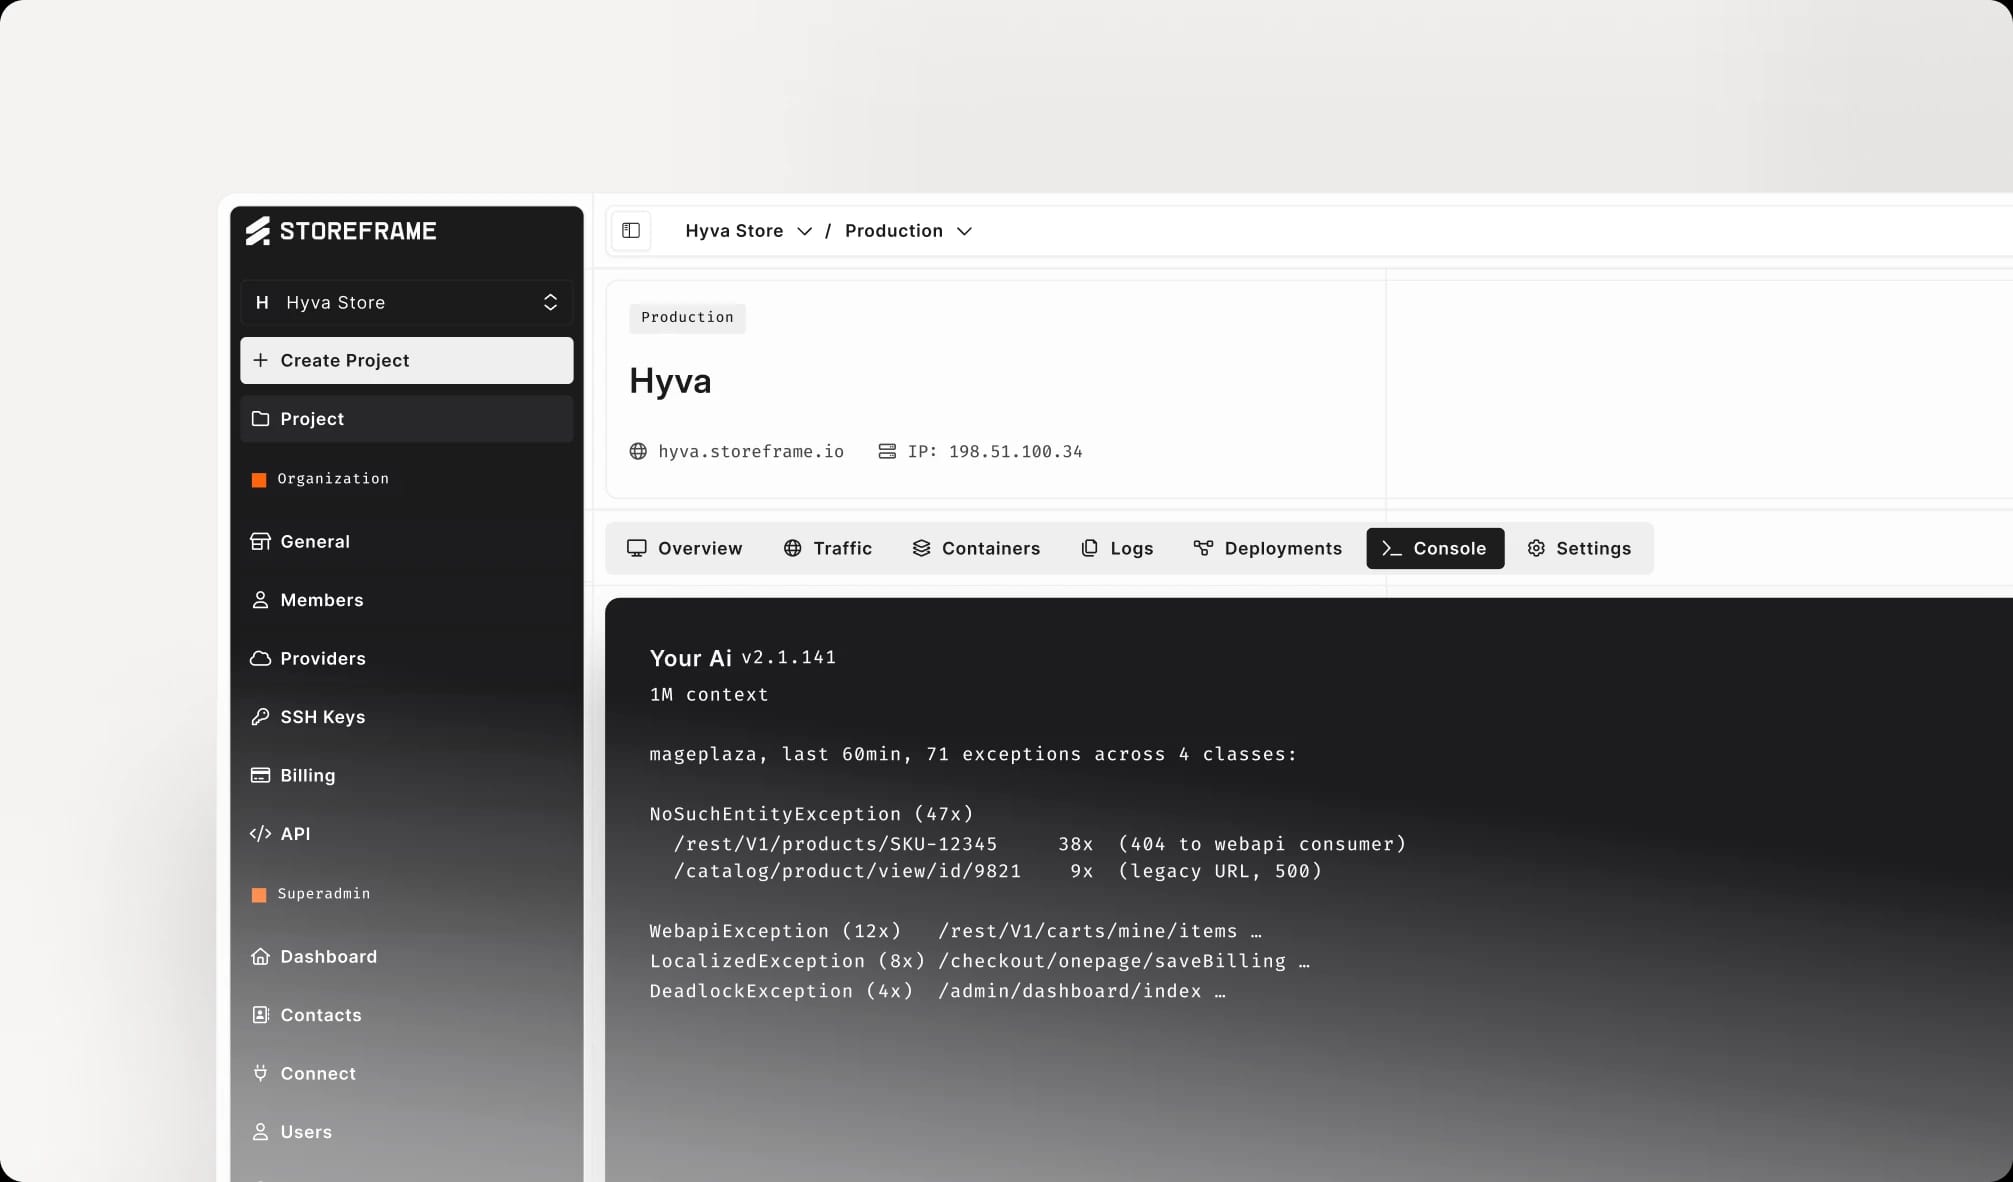
Pre-loaded knowledge, structured data, and a forensic audit trail. Claude Code lands ready to read your environment, not learn it.
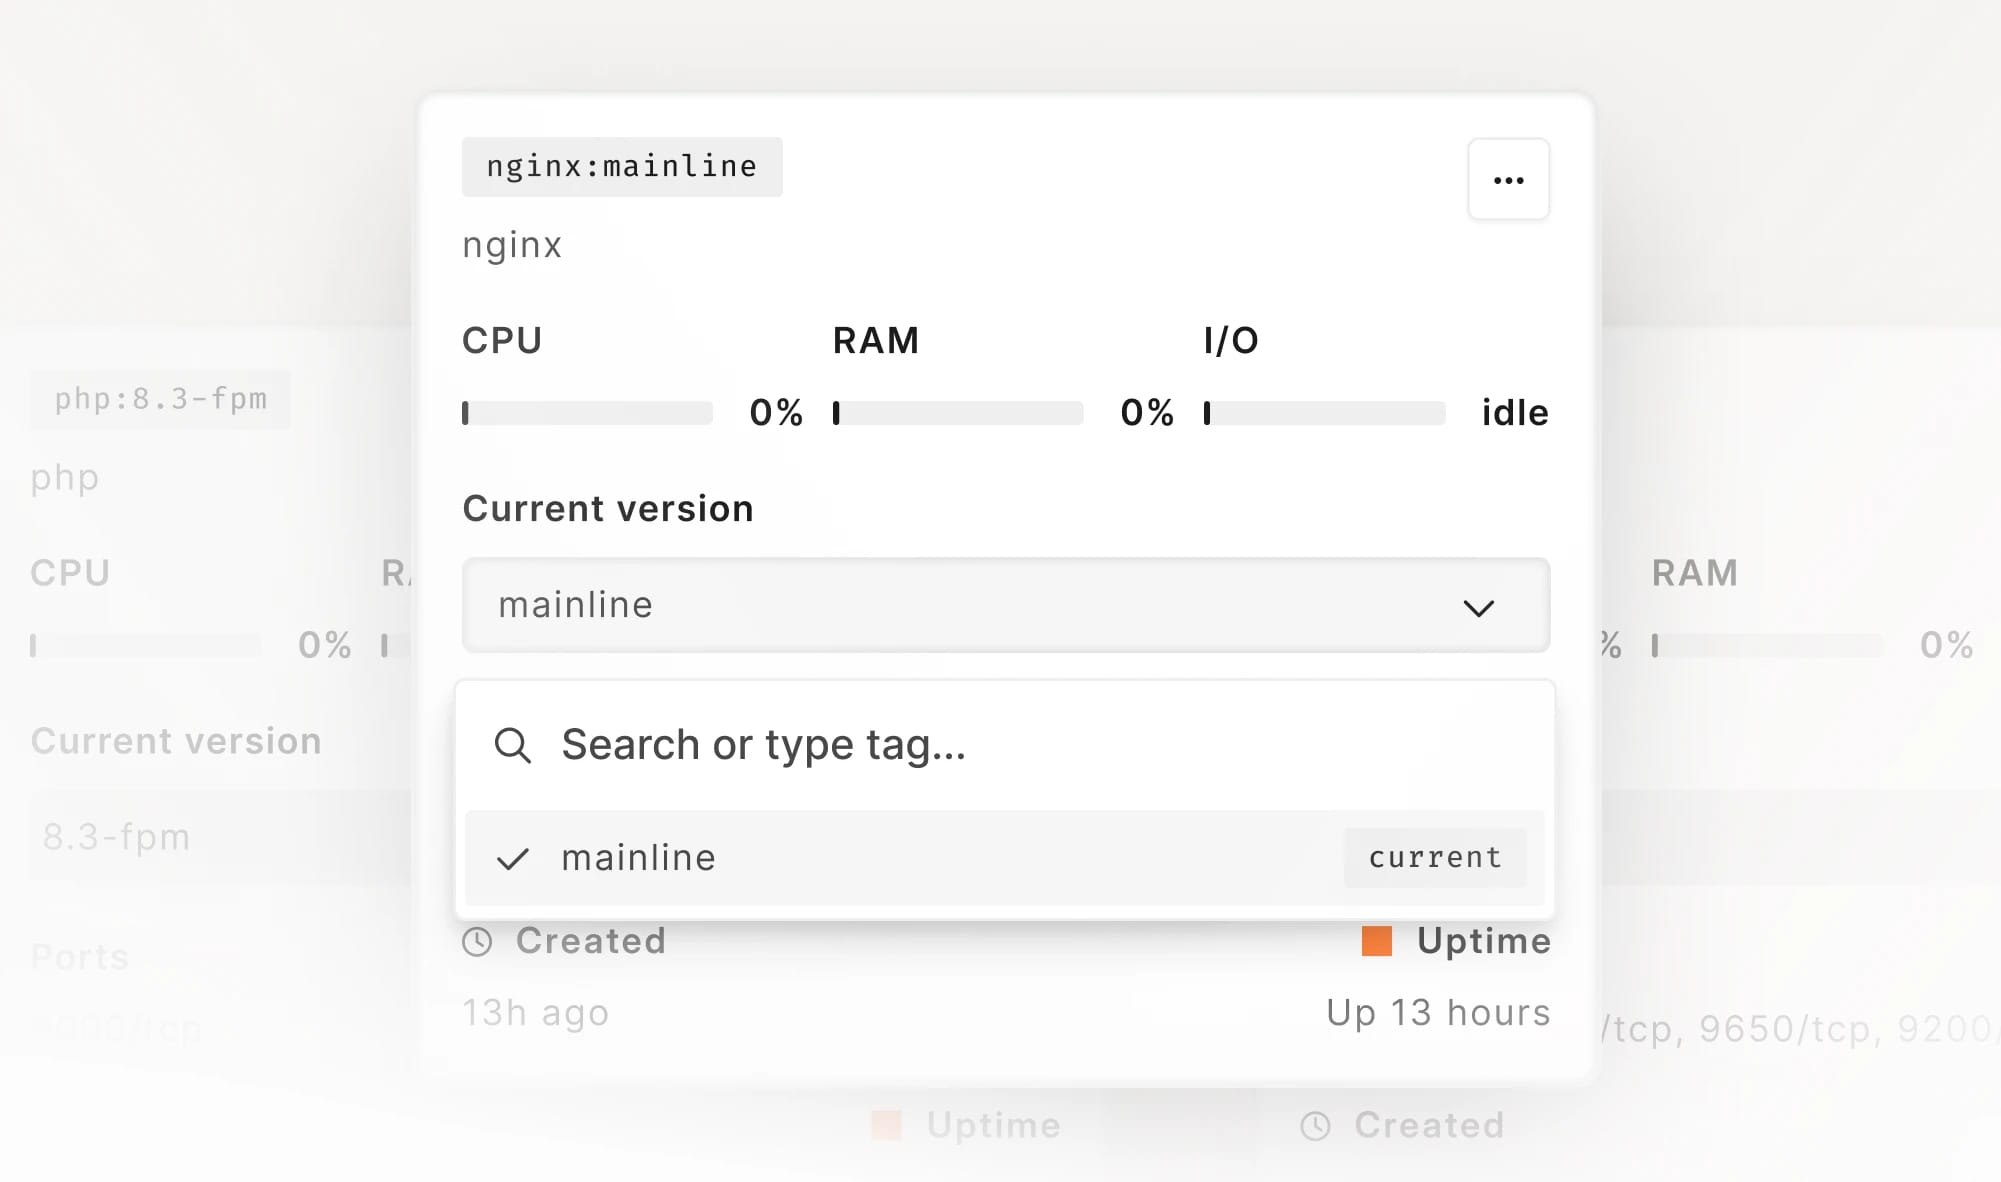
Containerized Stack & Tuning
Ten-plus isolated services per environment — OpenResty, Varnish, FrankenPHP, MariaDB, OpenSearch, RabbitMQ, more — auto-tuned to your server at provision and re-tuned automatically on resize.
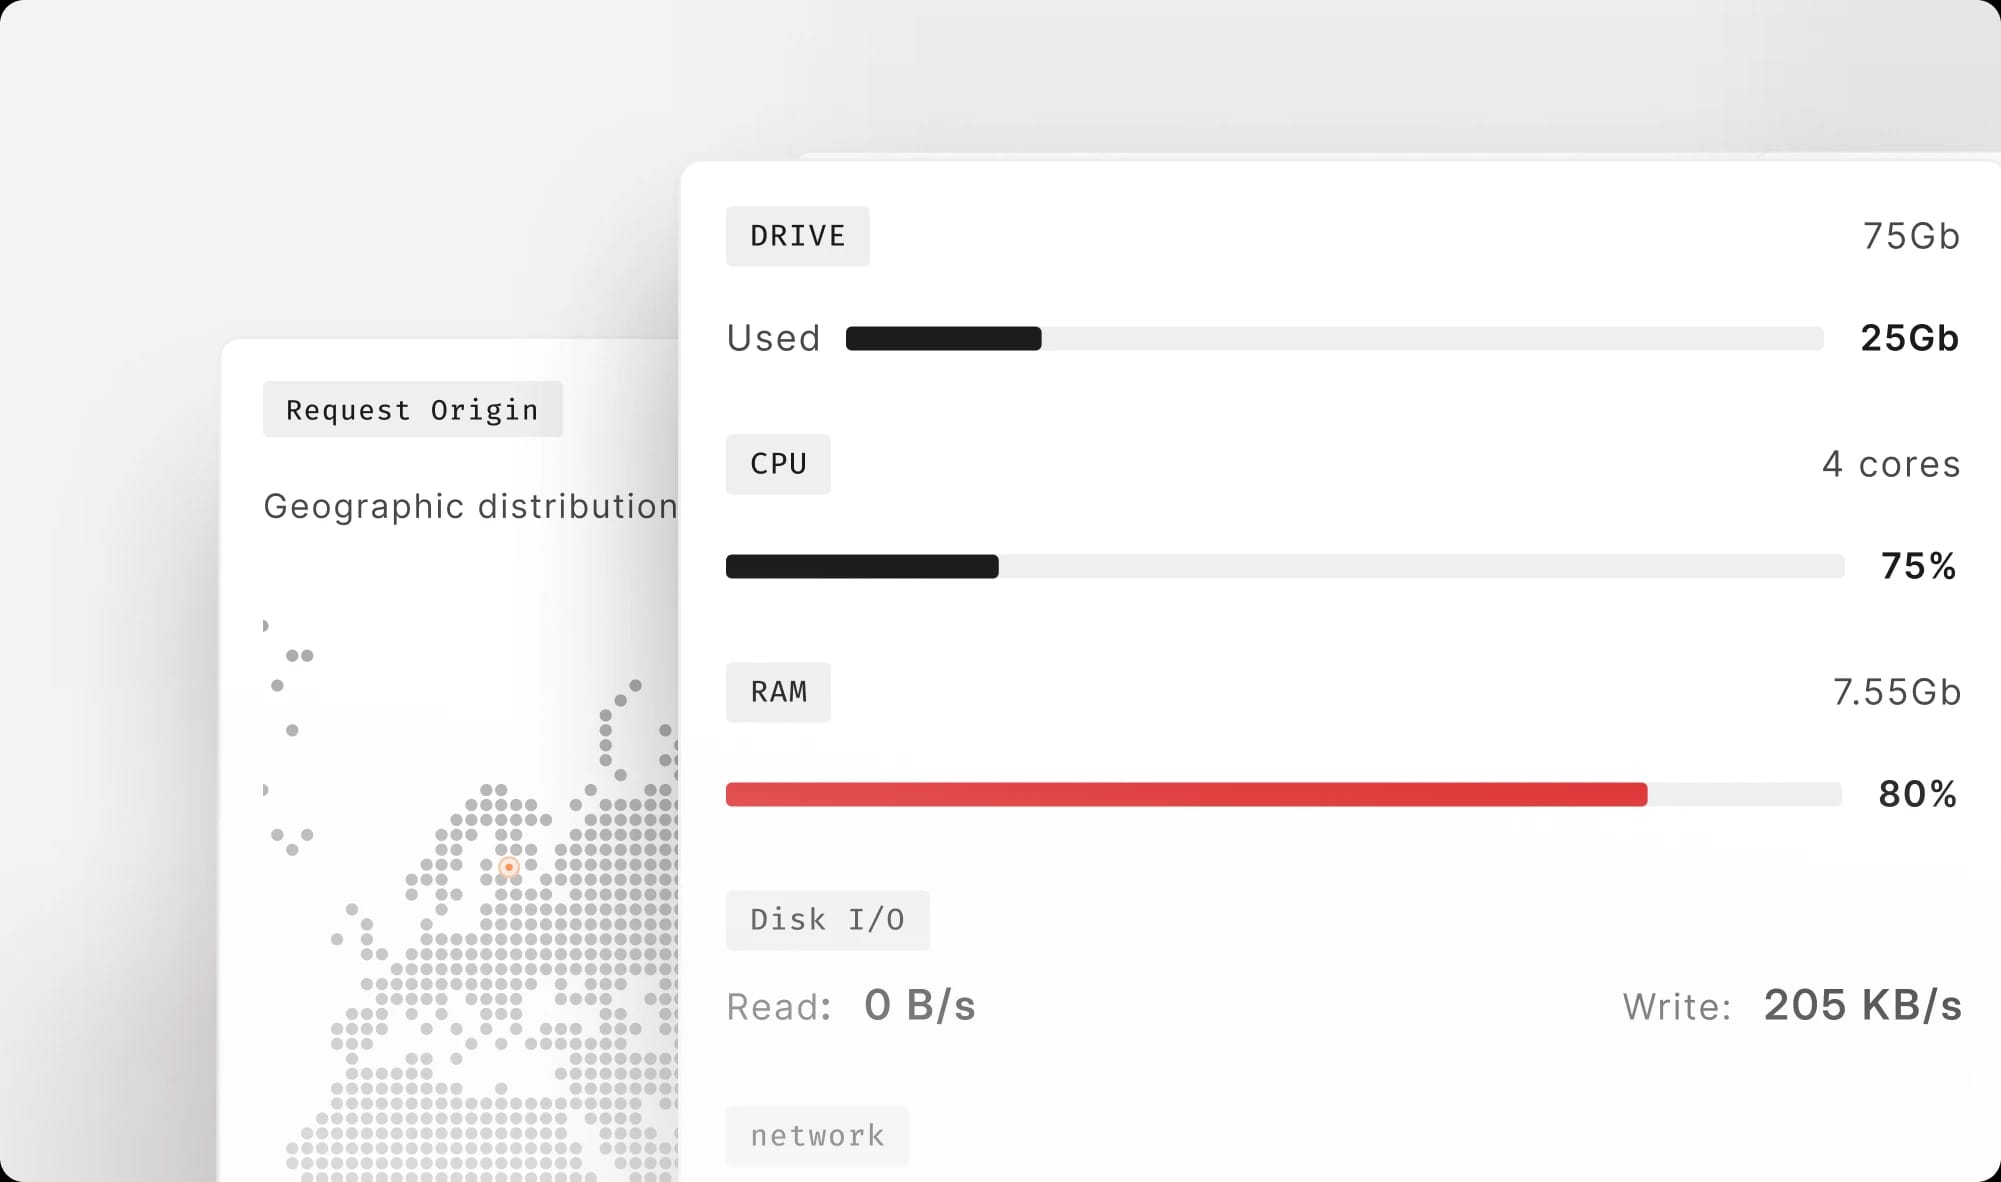
Real-Time Observability
Live logs, system metrics, eCommerce KPIs, traffic, and browser SSH — every signal from every environment flows into one HUB, refreshed on a 3-second cadence.
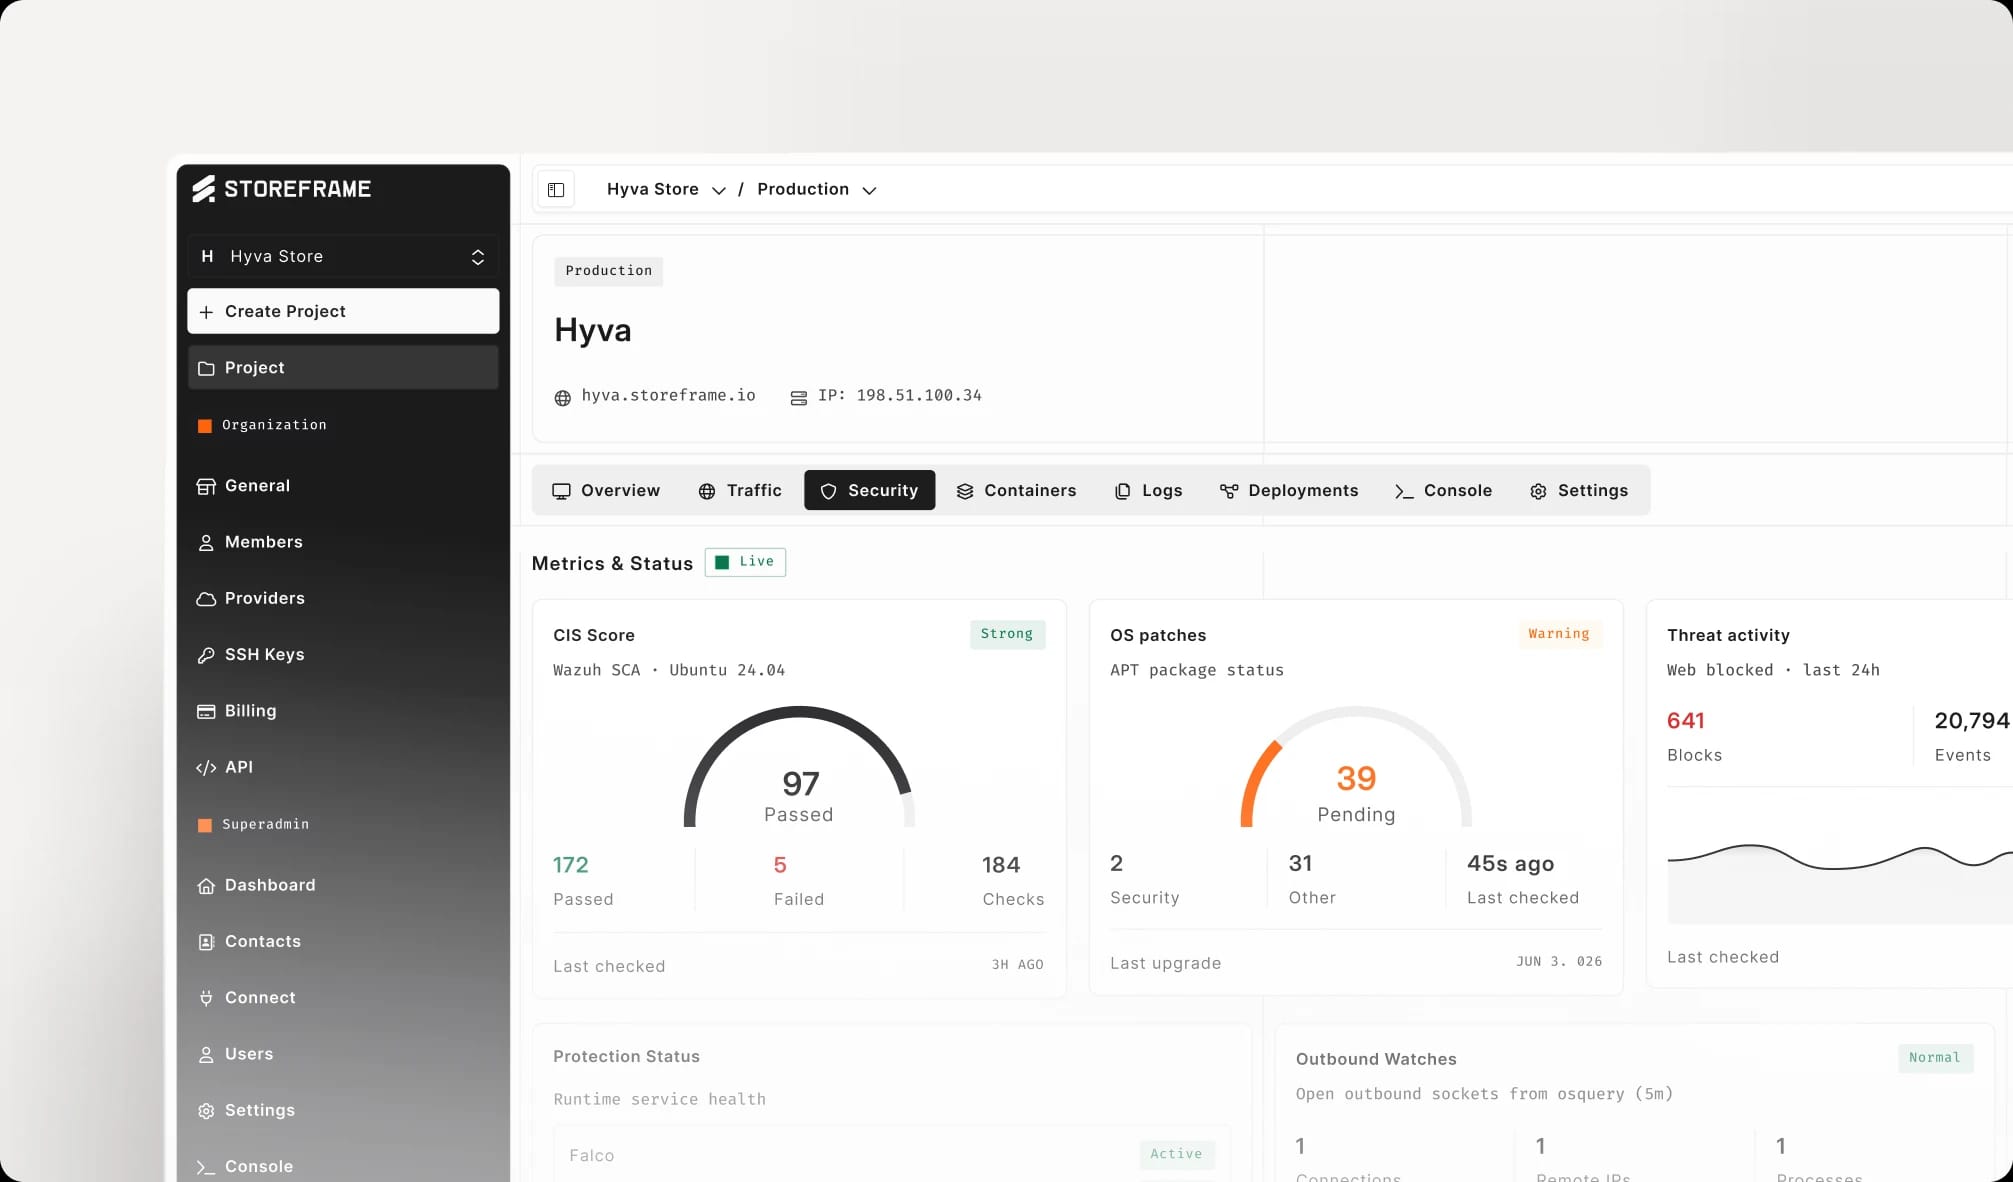
Built-In Security Layer
Firewall, WAF, threat intel, and a CIS-hardened OS — defense in depth on every environment by default, not a paid tier or an aftermarket bolt-on.
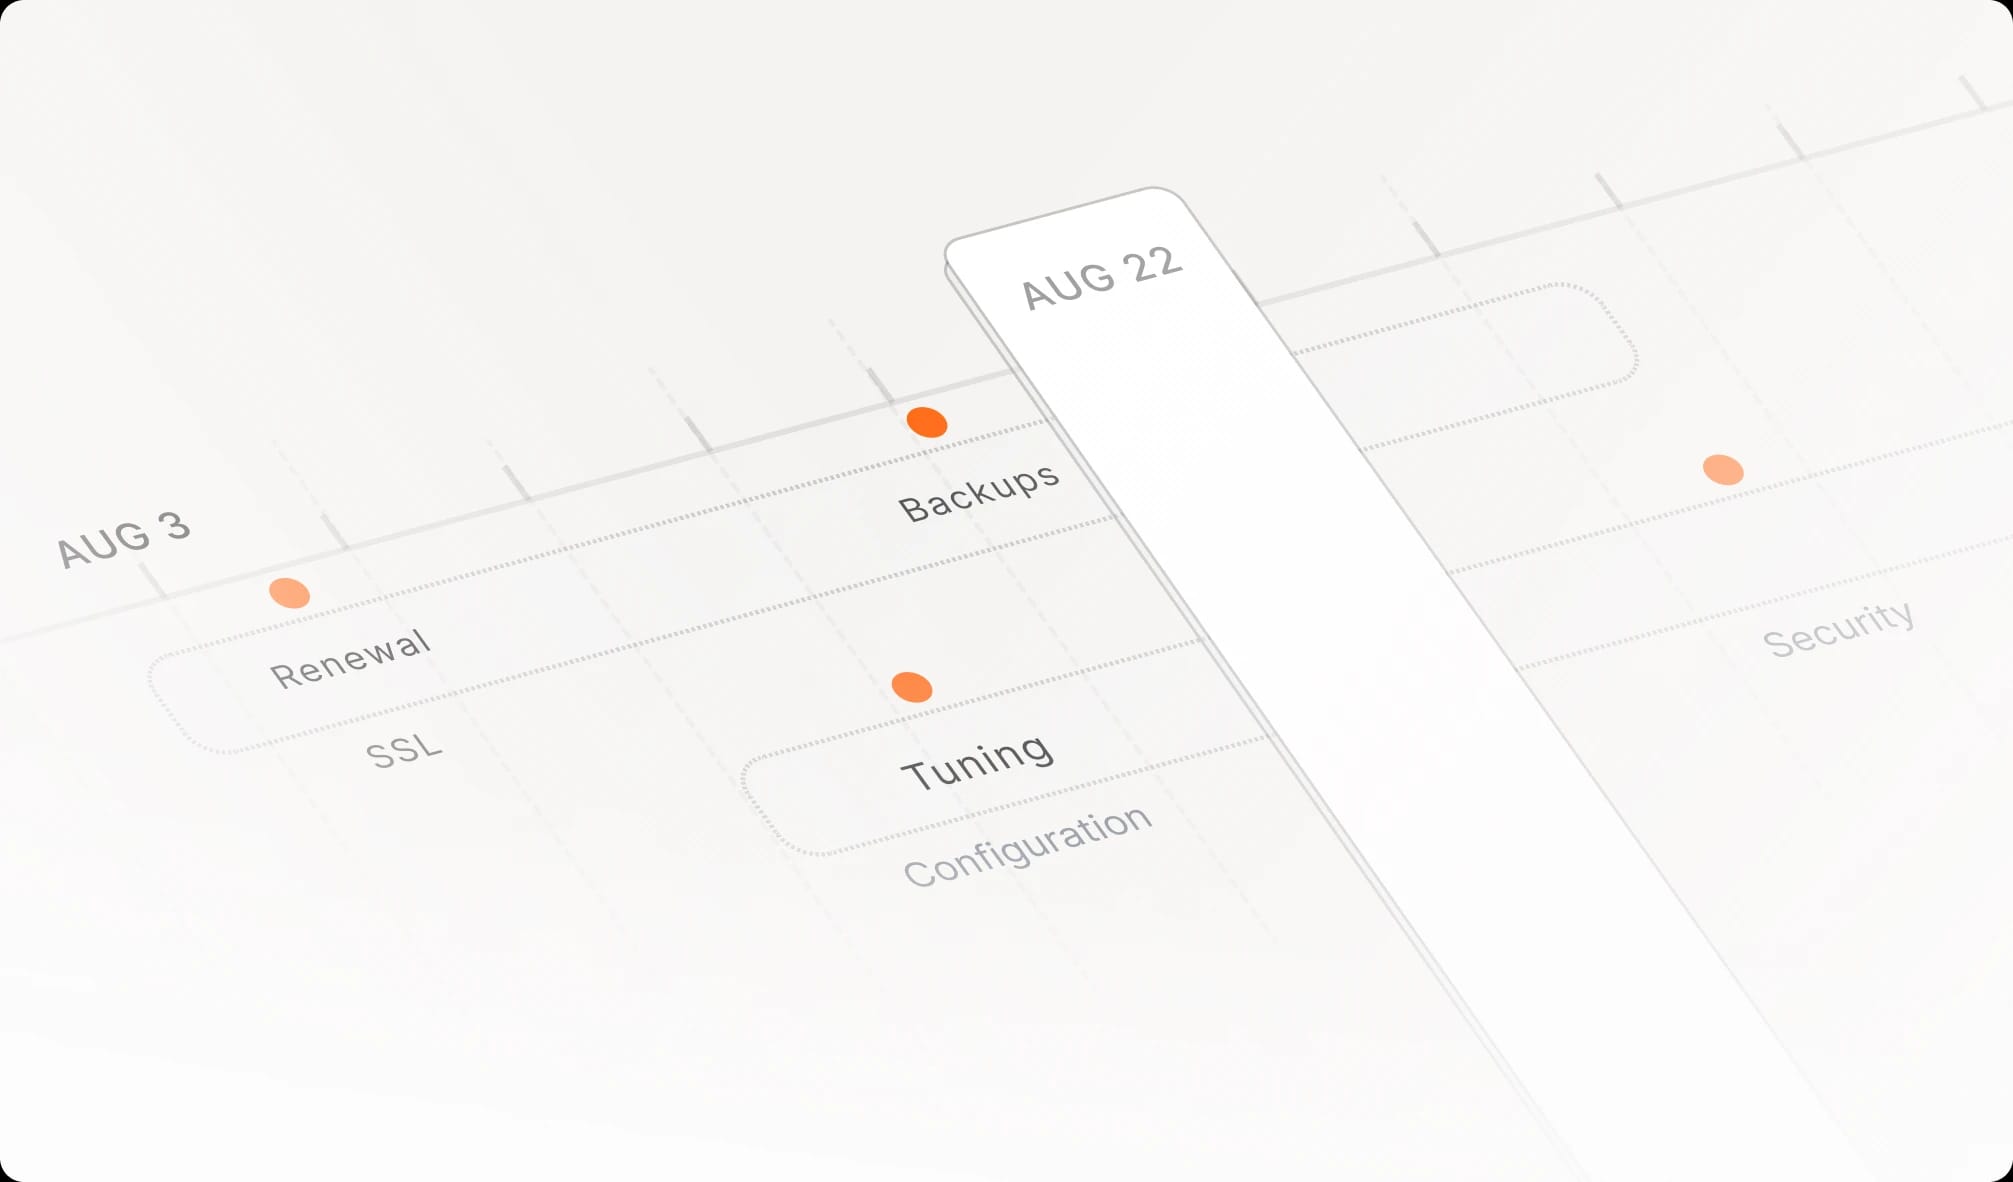
All Round Automation
SSL renewal, backups, provisioning, restores, security updates — the recurring ops work runs itself as background jobs, with retries on transient failures and audit on every run.
Built for Today's Standards
Built for Today's Standards
Many Magento control planes still operate like it's 1995 — locked servers, single-architecture, opaque internals. StoreFrame's foundation is current: native multi-arch, full root, audit-ready from day one.
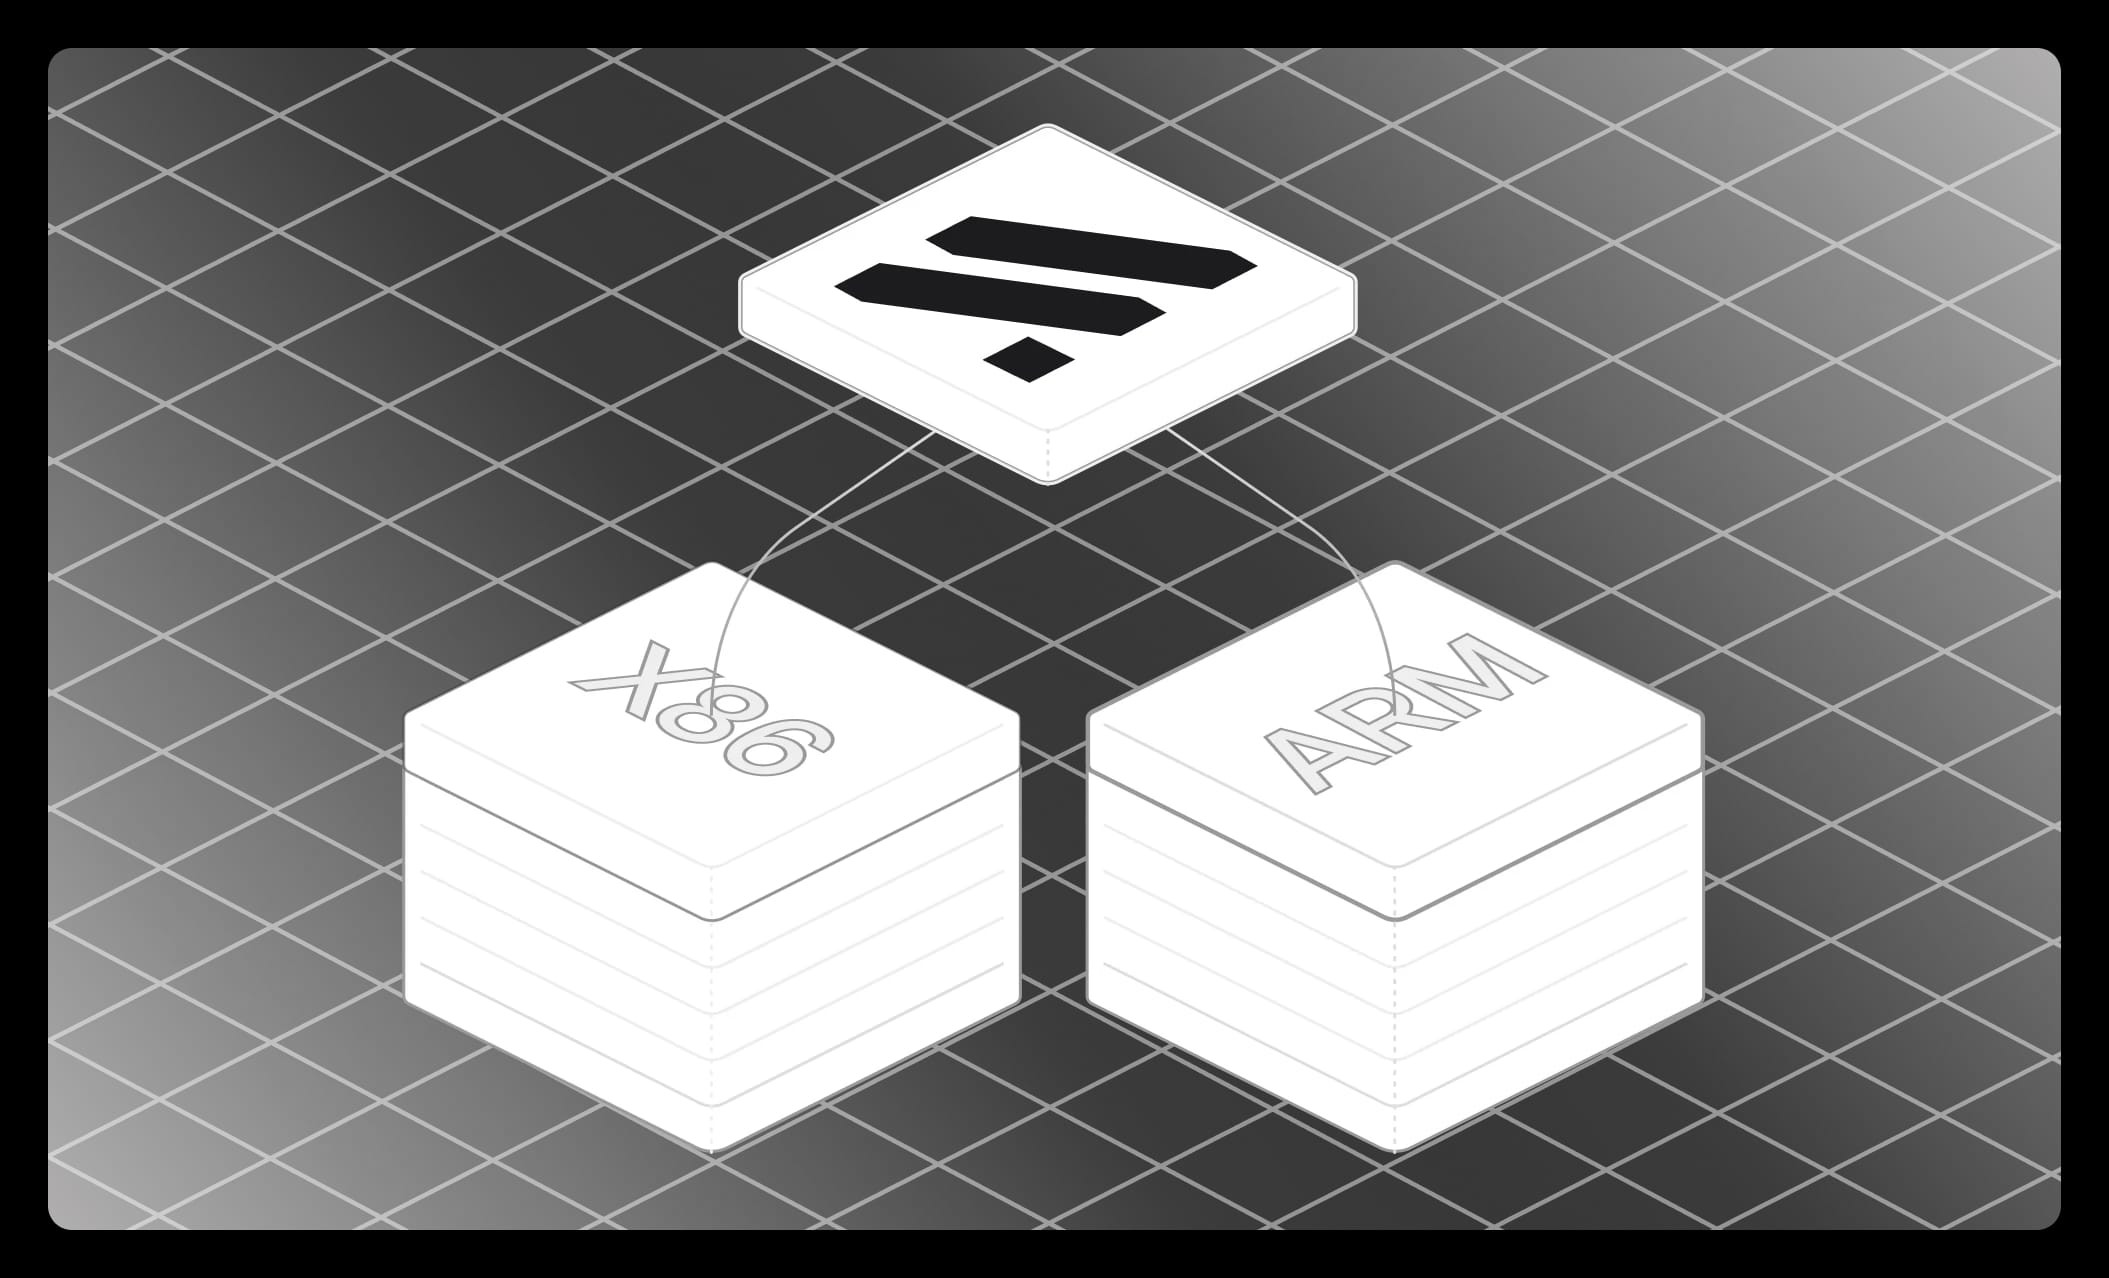
x86 and ARM Compatible
Provisioned on x86_64 (Intel/AMD) or AArch64 (ARM) servers — whichever your cloud sells. Multi-arch container images run natively across the entire stack, no emulation, no performance tax.
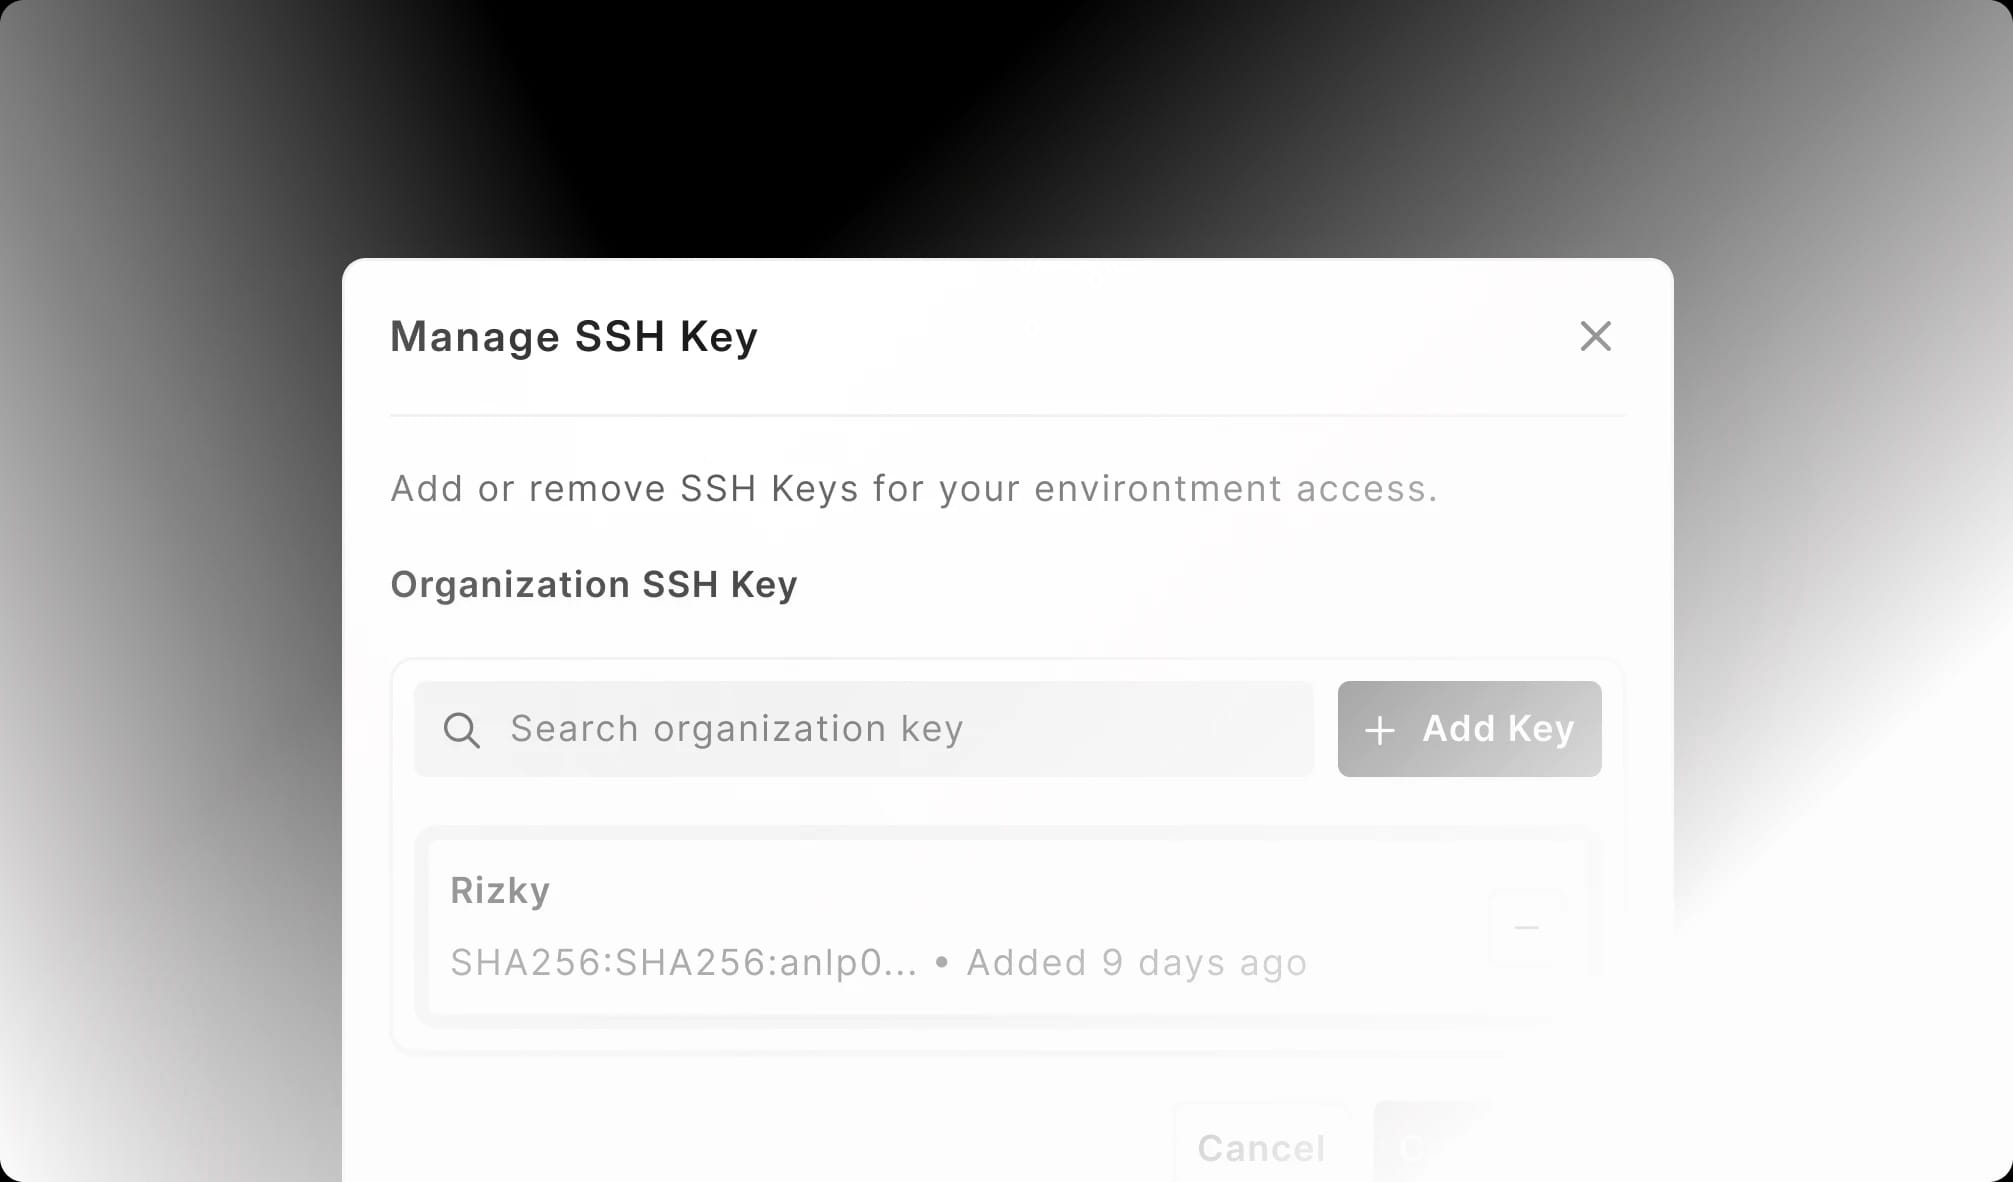
Full Root Access
Every server you provision gives you full root. SSH in directly, audit the host, run your own tools — the platform never locks you out of infrastructure that's already on your cloud account.